
IN BRIEF
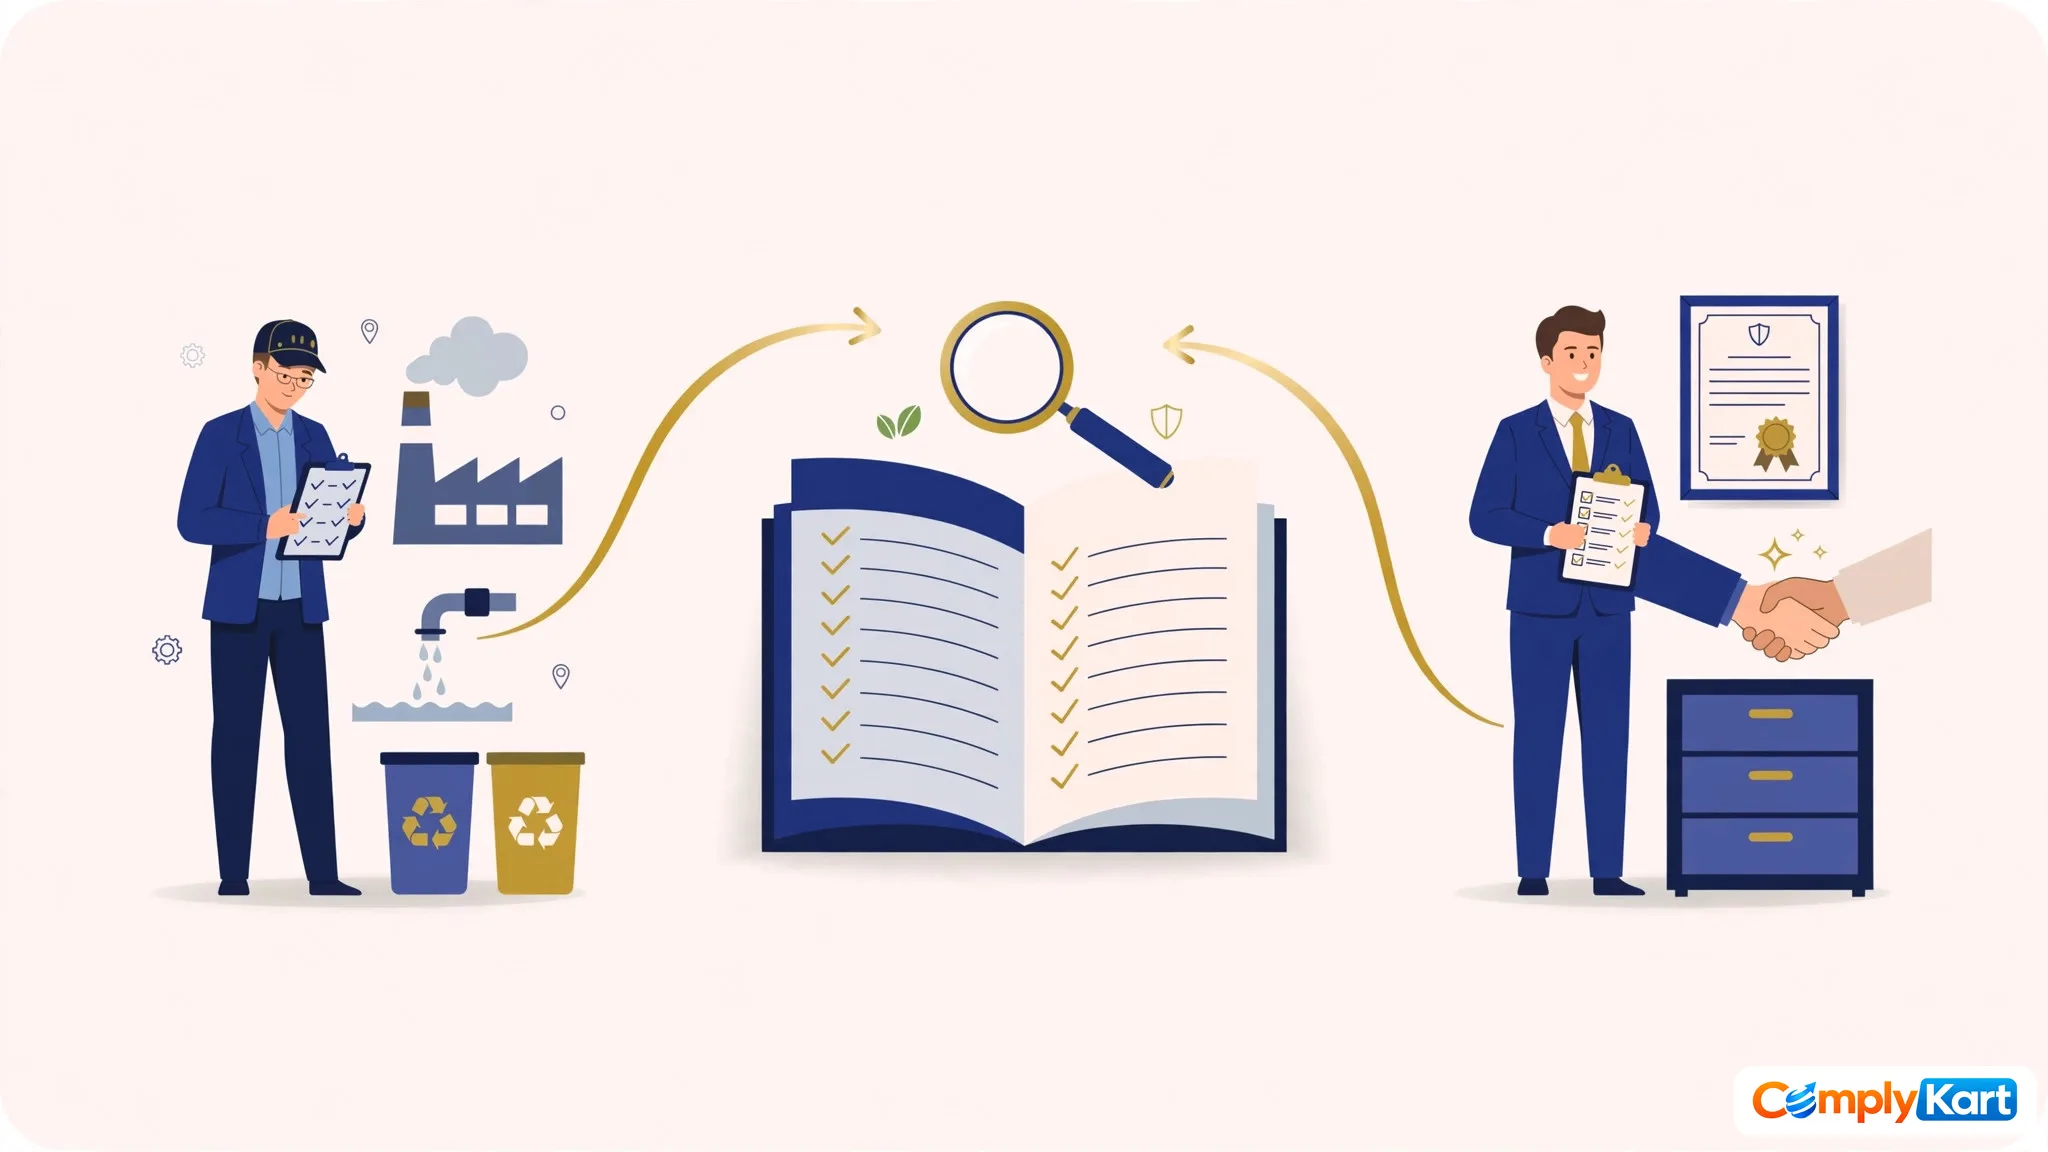
ISO 14001 documents are the scope, policy, aspects register, legal register, objectives, procedures and records that make up an environmental management system under ISO 14001:2015. The aspects register lists every way a site touches the environment and marks the significant ones, while the legal register lists the environmental laws and consents that apply and the evidence that they are met.
When an ISO 14001 auditor walks into your factory, they do not start with your machines. They start with your papers. They ask to see the register that lists every way your site touches the environment, and the register that lists every environmental law that applies to you. If those two documents are thin, copied from another company, or a year out of date, the rest of the audit gets harder. Get them right, and the audit feels like a conversation about a system you actually run.
Short answer: ISO 14001 documents are the scope, policy, aspects register, legal register, objectives, procedures and records that prove an environmental management system works. The two documents auditors read first are the aspects register (clause 6.1.2) and the legal register (clause 6.1.3). Everything else — monitoring records, audit reports, training records — exists to show those registers are alive, not forgotten.
What counts as an ISO 14001 document?
The standard uses one umbrella term: documented information, in clause 7.5. It covers two different things, and auditors treat them differently. Documents tell people what to do — a policy, a procedure, a work instruction. Records prove something was done — a waste manifest, a meter reading, a training attendance sheet. A procedure with no records behind it is a promise. Records with no procedure behind them are luck. Auditors look for both, linked together.
One surprise for first-timers: ISO 14001:2015 does not demand a quality-style manual, and it does not hand you a fixed list of documents to write. It names the documented information each clause requires — scope (4.3), policy (5.2), aspects and their impacts (6.1.2), compliance obligations (6.1.3), objectives (6.2.1), competence evidence (7.2), communication evidence (7.4), operational control information (8.1), monitoring results (9.1), compliance evaluation results (9.1.2), audit programme and results (9.2), management review results (9.3), and nonconformity records (10.2) — and then clause 7.5.1 adds whatever else your organisation itself decides is necessary for the system to work. That last part is where most companies either write far too much or far too little. The test is simple: if an auditor asks "show me how you do this," can you point to a document or a record? If the answer is a shrug, you have a gap.
The two registers auditors read first
Every other document in the file supports these two registers, or flows from them. Build them before you write a single procedure, because procedures written without them describe a factory that does not exist.
What does an aspects register actually contain?
An environmental aspect is an element of your activities, products or services that interacts with the environment — a chimney stack, a discharge drain, a diesel generator, a paint booth. The impact is the change that follows: air emissions, water pollution, soil contamination, resource use. The aspects register is the table that lists them all, site by site, and marks which ones matter most. Think of it as a map of every tap, chimney and bin in your premises, with a note on each one saying what leaves through it and where it goes.
A register an auditor can use has these columns: the activity or area, the aspect, the impact, the operating condition (normal, abnormal or emergency), the significance score under your own criteria, whether it is significant, the control in place, and the legal requirement linked to it, if any. One row might read: boiler house, stack emissions, air pollution, normal, significant, bag filter maintained monthly, consent to operate condition. Another: diesel storage, spill during unloading, soil and groundwater contamination, emergency, significant, bunded tank plus spill kit and drill. Rows without a control, or rows marked "not significant" with no reasoning, are the first things an auditor circles.
Walk the site to build it. A register written from a desk misses the solvent drum behind the maintenance shed and the DG set that only runs during power cuts. Auditors know this, which is why they cross-check your register against what they see on the shop floor. A copied register from a consultant's template, with another industry's aspects still in it, is worse than a short honest one — it tells the auditor nobody in your company owns the document.
How do you decide what counts as significant?
The standard does not hand you a scoring formula. Clause 6.1.2 says you must set your own criteria for deciding significance, apply them consistently, and keep the criteria themselves as documented information. Most companies score each aspect on two or three factors — how severe the impact is, how often it happens, and how likely it is to breach a legal limit or draw a regulator's attention — then set a cut-off above which an aspect is significant. What matters is not the maths. It is that the same criteria, applied by two different people, give the same answer, and that every significant aspect ends up with an objective, a control, or both. An aspect you scored as significant and then ignored is a finding waiting to happen.
Significant aspects drive the rest of the system. They shape your objectives under clause 6.2, your operational controls under clause 8.1, and what you monitor under clause 9.1. If your objectives talk about reducing water use but your register says water is not significant, or your register says solvent emissions are significant but no procedure mentions them, the system does not join up — and auditors are trained to spot exactly that.
What goes in a legal register?
The legal register, sometimes called the compliance obligations register, answers a plain question: which environmental laws apply to this site, what exactly do they require of us, and how do we know we are meeting them? Clause 6.1.3 requires you to determine your compliance obligations, work out how they apply to your aspects, and take them into account when you build the system. The register is where that thinking lives.
For an Indian factory, the register typically tracks the consent to operate from the State Pollution Control Board, with its conditions on air emissions and effluent discharge; authorisations for hazardous waste, e-waste or plastic waste where those streams exist; groundwater permission where a unit draws from a borewell; and any industry-specific rules for its sector. Each entry needs the same columns: the law or consent, the specific requirement, how it applies to your site, the person responsible, the renewal or reporting date, and the evidence of compliance — a consent copy, a return filed, a manifest. A register that lists law names but no dates, no owner and no evidence is a library catalogue, not a compliance tool. And it must be reviewed whenever a law changes or a consent is renewed, not once a year the week before the audit. If your consent to operate changed in June and your register still shows the old conditions in December, the auditor will find it before you do.
That review habit is also what clause 9.1.2 tests. At least once a year, you must evaluate whether you actually meet your compliance obligations, and keep the result as a record. The evaluation does not need a lawyer. It needs someone senior enough to read the register against the evidence — consents in date, returns filed, manifests matched — and write down the verdict, including the gaps. A clean verdict with no gaps, in a factory that missed a return, reads as fiction. Auditors trust a register that admits one overdue item and shows it being chased more than a register that claims perfection.
The rest of the file, in the order auditors expect it
Once the two registers exist, the remaining documents fall into place. The scope (4.3) states plainly which sites, activities and products the certificate covers — an auditor checks that the certificate's scope matches the factory they are standing in. The environmental policy (5.2) commits the company to protecting the environment, meeting its compliance obligations and improving continually; it must be available to interested parties, which in practice means displayed and shared, not locked in a file. Objectives (6.2.1) turn the significant aspects into targets with an owner, a deadline and a plan — "reduce" without a number, a person or a date is a wish, not an objective.
Operational controls (8.1) are the procedures for the significant aspects: how waste is segregated and handed to an authorised recycler, how chemicals are stored, how the effluent plant is run. Emergency preparedness (8.2) covers the spill, fire or release scenarios your aspects register flagged as emergency conditions, with a response plan and drills on record. If you outsource anything that affects a significant aspect — a waste handler, a contract housekeeping team — clause 8.1 expects you to control that too, through the contract and through checks. For factories weighing this against their existing setup, our ISO 14001 guide for factories walks through how consent-to-operate conditions and buyer audits connect to these controls.
The records auditors actually sample
Documents say what you do. Records prove you did it. Auditors sample records across the whole cycle, and they sample backwards: they pick a recent month and follow the trail. Monitoring and measurement results (9.1) — stack readings, effluent test reports, water and energy meter logs — with calibration records for the instruments that produced them. Internal audit reports (9.2) showing the full system was audited against its own schedule, with findings tracked to closure. Management review minutes (9.3) showing top management actually discussed audit results, compliance status, objectives and changing risks, with actions assigned. Nonconformity and corrective action records (10.2) showing what went wrong, what fixed it, and whether the fix held. Competence records (7.2) for the people whose work affects significant aspects — the effluent plant operator's training, the waste handler's induction. Communication records (7.4) for the environmental information you sent out and received, including complaints and how they were answered.
Two habits make records audit-proof. First, every record carries a date, a name and a version where it matters — an undated monitoring sheet is scrap paper. Second, records are retrievable in minutes, not hours. Auditors notice how long it takes you to find a document. A shared drive with a clear folder structure and a document register beats a shelf of binders nobody has opened since the last audit, and the standard does not require any particular software. Clause 7.5.3 only requires that documented information is available where and when it is needed, protected from loss, misuse or damage, and controlled for changes, retention and disposal. A small company with a tidy drive, a naming convention and a retention rule meets that clause. A large company with an expensive system nobody updates does not.
Five gaps that cost certificates
The same five findings appear in audit after audit. First, a stale legal register — consents renewed but never updated, or a new waste rule nobody added. Second, a copied aspects register with another company's processes in it. Third, documents with no version or date, so nobody can tell whether the shop floor uses the current procedure. Fourth, objectives with no plan behind them — a target nobody owns. Fifth, records stored in one person's laptop or inbox, unreachable when that person is on leave. Fix those five and you have fixed most of what a Stage 1 document review flags. Stage 1, the auditor's first visit, is largely a paperwork review: it tests whether the documented system is complete enough to audit at all. Companies that fail Stage 1 usually fail on the two registers, not on the factory floor.
Building it in the right order, and what it costs
Work in this order: walk the site and list aspects; score significance; build the legal register and check every consent and authorisation against it; write objectives for the significant aspects; write procedures only for the controls those aspects need; then set up the record folders — monitoring, audits, reviews, incidents, training — before the system starts running. Writing procedures first and registers second is how companies end up with a thick manual nobody reads and two registers nobody trusts.
On cost, be clear-eyed about what you are paying for. Our ISO 14001 certification consultancy runs ₹9,999 for the Standard tier (up to 25 employees) and ₹19,999 for Growth (26–100 employees), and that covers building exactly this documentation set with you. Certification-body audit fees sit outside that, charged at actuals, as our ISO 14001 cost and process guide explains in full. If you already run ISO 9001 and are adding 14001, the document-control and internal-audit machinery can be shared — our integrated management system guide shows where one set of records serves three standards. And if you want a quick sense of the wider compliance bill before you start, the compliance fee calculator puts a number on it.
Frequently asked questions
Do I need an environmental manual? No. ISO 14001:2015 removed the manual requirement that older standards carried. Many companies still keep a short manual because it helps new managers grasp the system in one sitting, but an auditor cannot raise a finding for not having one. They can raise one for a manual that describes a system nobody follows.
How often should the registers be updated? Whenever something changes — a new process, a new chemical, a renewed consent, a new rule — and formally reviewed at least before each internal audit and management review. A register updated only the week before the external audit reads as theatre, and auditors say so in their reports.
Can one aspects register cover two sites? Only if the sites genuinely share the same processes, and even then each site needs its own rows for what differs — different consents, different waste streams, different neighbours. One register with a "Site A / Site B" column works for a head office and a warehouse. It does not work for two factories making different products.
Can records be purely digital? Yes. The standard cares that records are controlled, retrievable and protected, not what medium they live on. Scanned manifests, spreadsheet meter logs and PDF audit reports are all fine, provided backups exist and access is limited to the people who need it. What fails is a single laptop with no backup and no access control.
What does the Stage 1 audit check in my documents? Whether the documented system is complete and coherent enough for a Stage 2 audit to be worthwhile: scope, policy, registers, objectives, procedures for significant aspects, and evidence that internal audits and a management review have happened. Gaps at Stage 1 usually mean Stage 2 gets postponed, not failed — which still costs you the timetable you promised a buyer.
The documents are not the system. The system is what your people do when nobody is watching — the segregated waste, the maintained filter, the spill kit that is actually stocked. But documents are how an auditor sees that system, and how a new manager inherits it. Build the two registers honestly, keep them current, and let every other document earn its place by pointing back to them. That file will pass an audit. More importantly, it will describe a factory you recognise.


Comments
No comments yet — ask the first question below.
Join the discussion
Questions go straight to our expert desk. Comments appear after a quick review — no spam, no noise.